Unified Threat Detection & Incident Handling
Detect faster and respond smarter: AI-enhanced detection, correlation and analyst-led incident handling.
Unified Threat Detection and Incident Handling brings detection, response and correlation together in one service, so you detect faster and respond smarter. AI-enhanced detection and hands-on, analyst-led response contain even the most complex threat actors and their most sophisticated techniques.
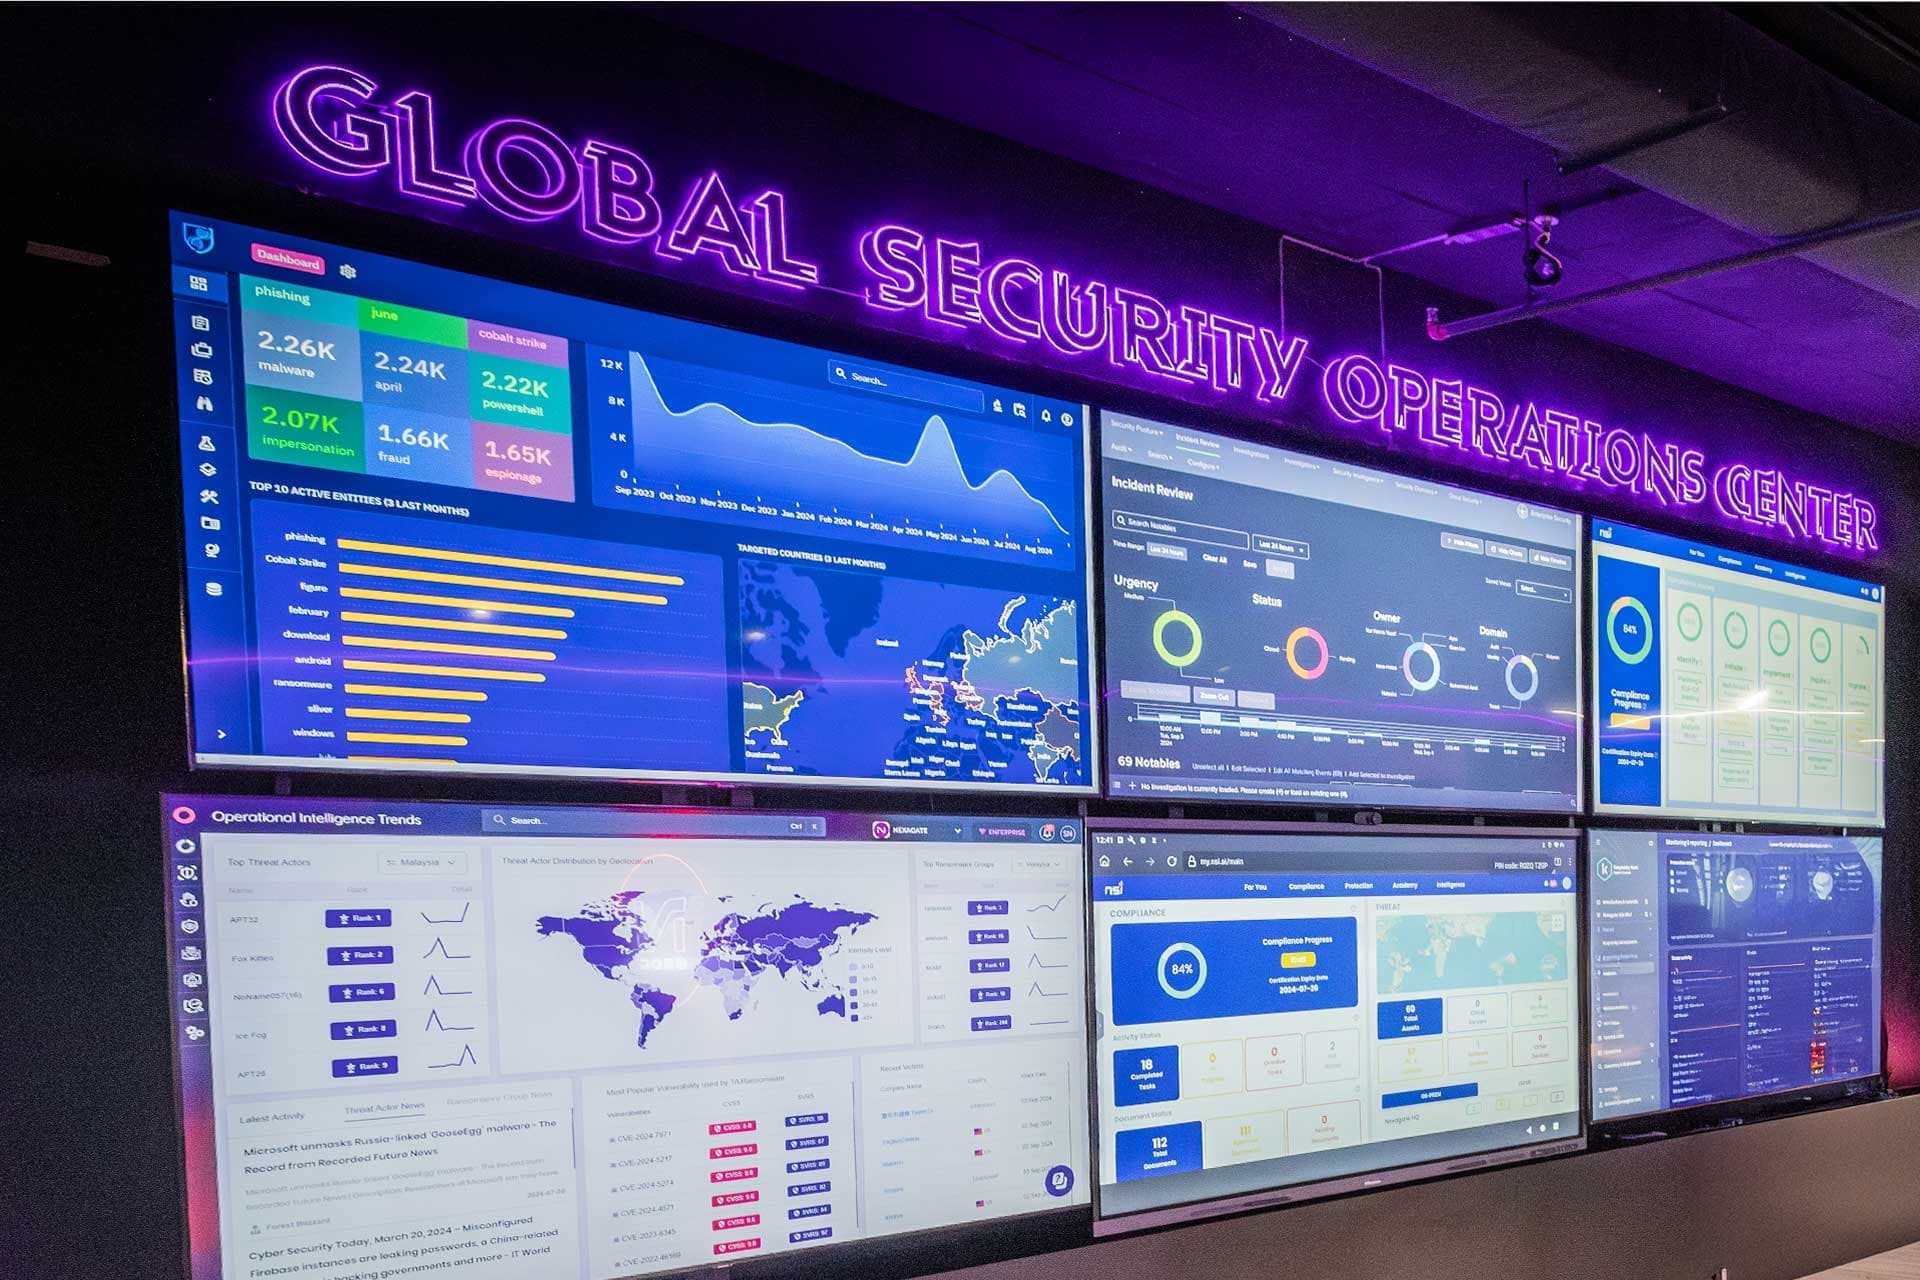
Our Global SOC correlates events from across endpoints, network, cloud and web for the most complete view of your security posture, without you operating multiple consoles. Machine learning classifies alerts on arrival so analysts start with the ones that matter, and detection is enriched with threat intelligence beyond any single feed. Validated incidents are contained in real time, digital forensics support investigation and recovery, and proactive threat hunting reduces adversary dwell time. Every incident is managed in NSI Incident Management for structured handling and SLA tracking.
Detect · Respond · Correlate
SIEM, analytics and behavioural detection, with machine-learning triage so analysts start with the alerts that matter.
Events correlated across endpoints, network, cloud and web so related activity surfaces as a single incident.
Automated and analyst-led containment isolates hosts and stops threats spreading in real time.
Digital forensics and incident response to investigate, contain and recover from confirmed incidents.
Proactive hunting across your environment surfaces stealthy activity the tooling alone would miss.
Key benefits
How we work
A consultant will scope the environment, size the service and come back with a quote, usually within one business day.