Managed Security
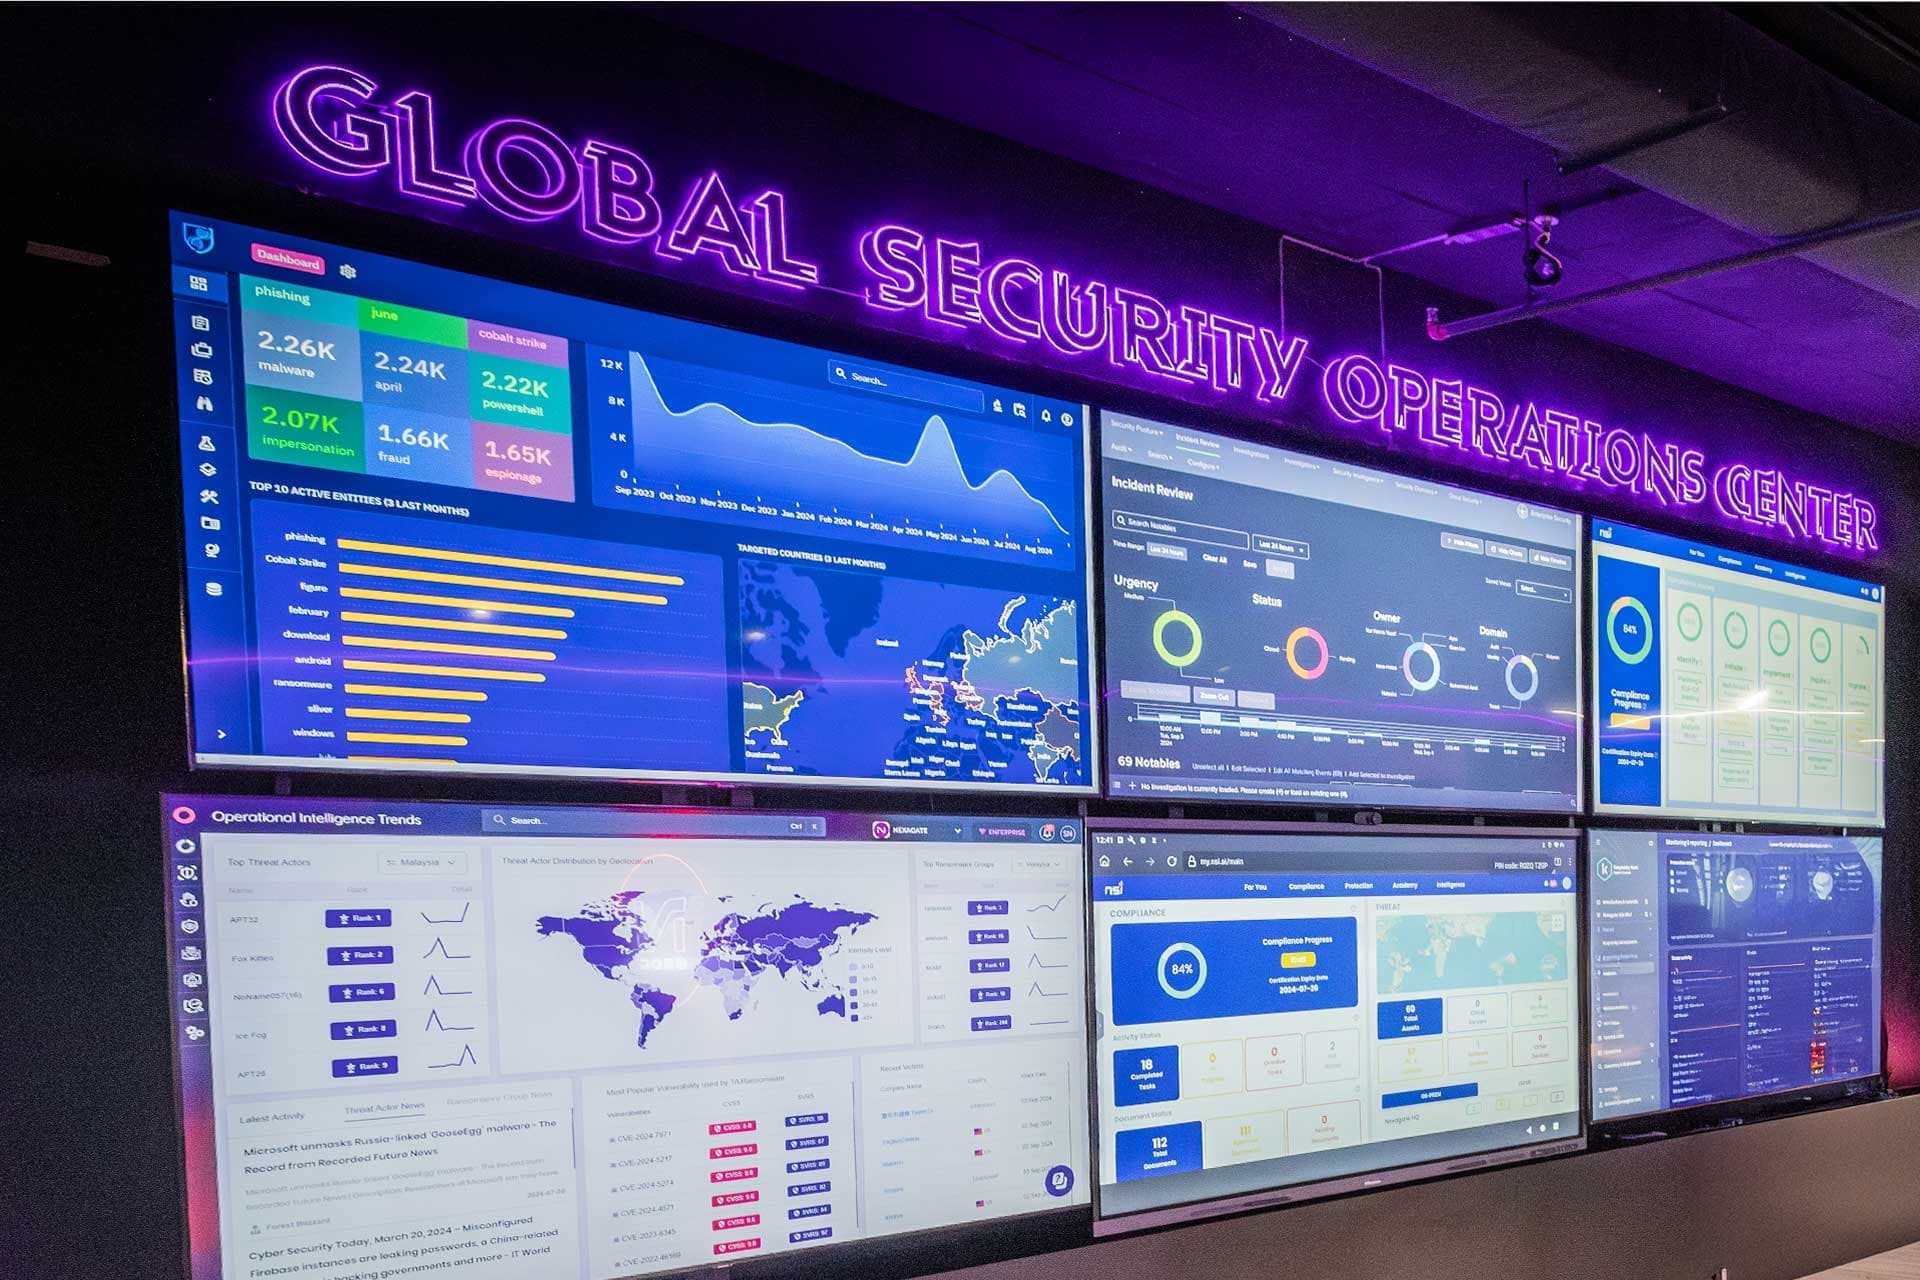
24/7 cybersecurity monitoring and incident response, delivered from the Nexagate Global SOC.
Investing in cybersecurity technology is only the first step. Effective security requires continuous monitoring, expert oversight, ongoing optimisation and the ability to respond quickly when threats emerge. Our Managed Security services bridge this operational gap, providing organisations across financial services, government, telecommunications, healthcare, utilities and manufacturing with the expertise and capabilities needed to protect their environments around the clock.
SOC-as-a-Service
SOC-as-a-Service delivers comprehensive, subscription-based security operations through our Global SOC. You get experienced consultants, proven processes and advanced detection across four core services, without the cost and delay of building an equivalent capability in-house.
- Continuous 24/7 Monitoring: Round-the-clock threat triage and validation by experienced security analysts and consultants.
- Tailored Detection Engines: Custom-tuned to your unique environment at onboarding and continuously optimised.
- Structured Escalation Protocols: Pre-defined communication paths ensuring critical incidents instantly reach the right stakeholders.
- Playbook-Driven Remediation: Actionable step-by-step guidance and event-specific incident response playbooks.
Everything in this pillar
Engage individual services based on your needs, or bring the full suite together under a single engagement, unified through one platform.
24/7 Monitoring & Escalation
Always-on monitoring across users, devices, network, cloud and web, with proactive escalation from our Global SOC.
Detection & ResponseThreat Detection & Incident Handling
Detect faster and respond smarter: AI-enhanced detection, correlation and analyst-led incident handling.
Threat IntelligenceIntelligence-Driven Defence
Stay ahead and be better prepared: turn global and local threat intelligence into action.
Professional ServicesProfessional Services
Build capabilities for stronger security across people, process and technology.
Not sure where to start?
Most clients begin with 24/7 Monitoring & Escalation and add capabilities as the environment grows.
Talk to a consultant →
One platform. Every service. Complete visibility.
Every service in this pillar reports into NSI. You see the modules that matter to the work you have bought, the same view our analysts work from. Patented in Malaysia and Brunei.
See the full platform →Nexa Incident Management (NIM)
Structured incident management and SLA tracking across SIEM, MWSS, MDR and service requests, with our analysts and your team on the same ticket.
TI Hub: Threat Intelligence
Curated threat intelligence with an AI analysis layer over the feeds.
NSI Protection
Endpoint, WAF and DDoS controls with defacement and brand monitoring, managed from one console.
Intelligence layered into the service.
Automation first, intelligence on top. These components run in production today. Our analysts still make the call, but they stop doing the lookups by hand.
SIEM alert triaging
LiveML classification applied to Splunk alerts on arrival, so analysts start with the ones that matter.
Automated OSINT enrichment
LiveIndicators looked up across multiple intelligence sources automatically, instead of tab by tab.
TI Hub intelligence layer
LiveAnalysis over curated threat feeds, surfacing what is relevant to your environment rather than everything.
A consultant will scope the environment, size the service and come back with a quote, usually within one business day.